




CovertSwarm
About CovertSwarm
If you release code, hire people, open new premises or change your board more often than you attack yourself, you are not keeping pace with your own risk. CovertSwarm was founded in 2020 on that argument, frustrated that organizations relied on occasional penetration tests, thick reports and long gaps in between.
The Swarm runs realistic attacks across digital, physical, and social environments, then shows how weaknesses chain into paths an attacker could use against the business.
What we write about
- Continuous offensive security testing: Why occasional testing can’t keep pace with how often your organization changes.
- Emerging threats: New attack techniques and what they could let an attacker do to your organization.
- Offensive AI and AI security: Prompt injection, multi-agent risk and how attackers can turn AI and agentic systems against the organizations running them.
- Red teaming and adversary simulation: Chaining weaknesses into the attack paths a real adversary would follow.
- Regulatory threat-led testing: CBEST, STAR-FS and threat-led testing, from a team with CREST accreditation for both.
- Physical security and social engineering: Getting into buildings and past staff, and what that access exposes.
- Vulnerability research: Flaws in software and systems, and what an attacker could do with each one.
Latest posts
Exploring the Kubernetes Architecture from an Offensive Viewpoint (part 1)
Explore the essentials of Kubernetes: From its Google origins to a key tool in modern cloud-native development, learn about its architecture, API server, nodes, and security aspects.

Persistence Attack in Active Directory: The Golden Ticket Attack
Delve into the Golden Ticket Attack in Active Directory: a key APT method. Discover its workings, countermeasures, and detection to protect your network.
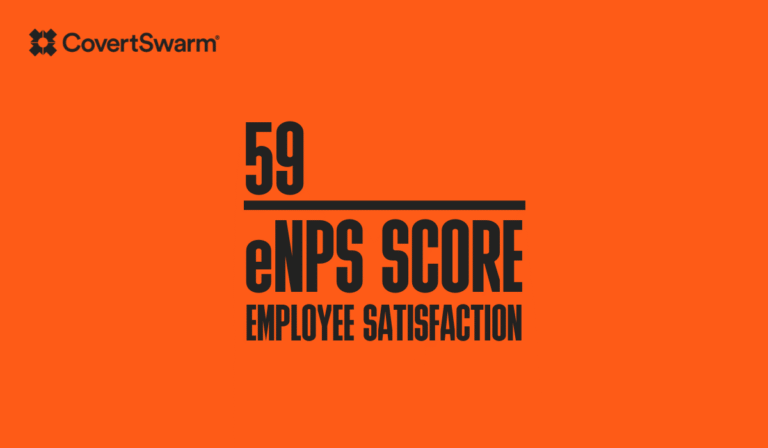
Our first Employee Net Promoter Score in review
CovertSwarm ranked as one of the leading industry employers after recording our first ‘excellent’ score
CovertSwarm named on the Startups 100 Index
Startup.co.uk has recognized us as one of the UK’s leading start-ups and part of the next generation of game changers.

CovertSwarm strengthens leadership team with three key senior appointments
We're preparing for another year of growth in 2024
What is Breach and Attack Simulation (BAS)?
Read our guide to find out what Breach and Attack Simulation (BAS) is, how it works, why and how it’s important, and some best practices.
What is vulnerability scanning and why is it important?
Read our comprehensive guide on vulnerability scanning, including what it is, why it’s important, how it works & best practices for organizations.
We’ve been named a CISO Choice Awards finalist
The program recognized CovertSwarm as one of the world’s leading cybersecurity solutions
Web application vulnerability scanning, in the palm of your hands
At CovertSwarm we pride ourselves on being able to provide the Portal as a centralized platform for managing and identifying risk to your organization. Following on from our recent blog post on why web application security and why it is…
What is web application security, and why is it important?
Read our guide on web application security, which includes what it is, why it’s important, how it works & best practices & useful strategies.
How to create a strong password and essential best practices
Read our complete guide on how to create a strong password & some essential best practices to level up your cybersecurity.
What is attack surface management and how does it work?
Read our blog to discover what attack surface management is, why it’s important in cybersecurity & why organizations need our Portal.
What is a purple team in Cyber Security?
Read our blog to find out what a purple team is & the difference between them & red & blue teams & why your organization needs one.
How to become an ethical hacker
If you’re looking to become an ethical hacker, read what skills, experience & certifications you need & how to apply at CovertSwarm.
What are insider threats and how do you prevent them?
Read our guide to understand what you need to know about insider threats, why they’re dangerous & how to identify, respond to & prevent them.
Incident response: a comprehensive guide
Read our blog to find out everything you need to know about incident response, including what a plan involves & steps you should take.
What is IT infrastructure, and why is it important?
Read our guide on IT infrastructure to find out what it is, why it’s important, how it works, its benefits & challenges & much more.
What’s the difference between red teaming and penetration testing?
Read our blog to find out the differences between red teaming & penetration testing & how to choose the right approach for your cybersecurity.
What’s the difference between a red team and a blue team?
Read our blog to find out what the differences are between a red & a blue team & what their roles and responsibilities are.
What is patch management and what are the benefits?
Read our blog to find out what patch management is, why organizations need it, best practices & some commonly asked questions.
Digital Forensics and Incident Response (DFIR): the ultimate guide
Read our complete guide on Digital Forensics & Incident Response (DFIR) to find out what it is, why it’s important, how it works & more!
Denial of Service (DoS) attacks: a complete guide
Read our complete guide to find out what Denial Of Service (DoS) attacks are, how they work & how to identify, respond to & prevent them.
What are evil twin attacks and how do you prevent them?
Read our blog to find out what evil twin attacks are, how they work, why they’re dangerous & how to identify, recover from & prevent them.
What is fuzzing and how does it work?
Read our complete guide to find out what fuzzing is, how it works, its advantages & disadvantages & best practices for fuzz testing.