




Constant Cyber Attack™
Outpace cyber threats with an offensive security subscription that keeps your whole organization under constant attack across digital, physical and social vectors.
Over 100 security leaders subscribe to CovertSwarm.
CovertSwarm named in the Gartner® Hype Cycle™ for Security Operations, 2026
The threat.
Would your security program survive an attack?
You’ve bought the tests, the tools and the scanners. You tell them where to look, and they’ll tell you what they found. None of them tell you what will break your business, because none of them act like a real attacker with intent.
You don’t need more findings. You need proof of where you really stand. For your board. For your regulator. For yourself. You need confidence that you’re preparing for the right war.
When did you last have that confidence?
Attackers don’t care about scopes.
Threat actors will target your whole organization: your people, your systems, your suppliers, and the parts you don’t even know exist.
They are only focused on impact.
A test hands you a list of findings. Attackers focus on what hurts you: your data, your money, your reputation. They will do whatever it takes.
They only need to be right once.
You have to defend all of it, every day. They just need the one gap you missed, and AI now helps them find it in hours, not months.
The only way to be confident is to face a real attacker.
We become the threat. Your CovertSwarm subscription gives you a team of elite ethical hackers augmented by agentic tools, that thinks, acts and strikes like a real attacker.
Your Swarm attacks your organization using digital, physical and social methods to find, chain and exploit weaknesses before a real attacker does. Then we show you how to fix them.
You’ll know exactly where you stand, with proof for your board, your regulator and yourself. Over 100 security leaders subscribe to CovertSwarm.
Are you ready? Let’s find out.
Digital, Social, Physical.
Your Swarm attacks across digital, physical and social vectors, chaining weaknesses to prove what a real attacker could achieve.
Constant pressure.
Your Swarm keeps attacking as your business evolves, adapting to changing systems, people and risks. Constant pressure, not a one-off test.
One subscription is all you need.
Combine penetration testing, red teaming and ongoing attacks in one subscription. One Swarm proving what’s exposed and what to fix.
How it works
Your subscription starts with your Attack Thesis: what matters most, and what adversaries would target first.
Your Swarm then runs realistic attacks against your whole organization in continuous cycles within agreed guardrails and without disruption to your operations.
Recon
We combine open-source intelligence and agentic reconnaissance with expert analysis to identify the threats that matter most to your organization. That intelligence shapes our attack plans, with new risks pursued as they emerge.
New risks enter scope as they emerge.
Expert analysis on your threats.
OSINT + Agentic reconnaissance.
Threat intelligence informs attack plans.
Attack
Based on intelligence or strategic goals, we build and execute custom Attack Plans. We chain weaknesses and exploit every route.
Custom built plans target your actual risk
Chained across digital, physical and social
Led by humans with agentic capability
Point the Swarm at your priorities
Remediate
We notify your team about discovered risks in real-time and provide guided remediation. Get evidence of what held, and what needs work.
You’re notified while the risk is live
Guidance in Slack and Jira
Findings inform the next attack cycle
Direct access to the Swarm
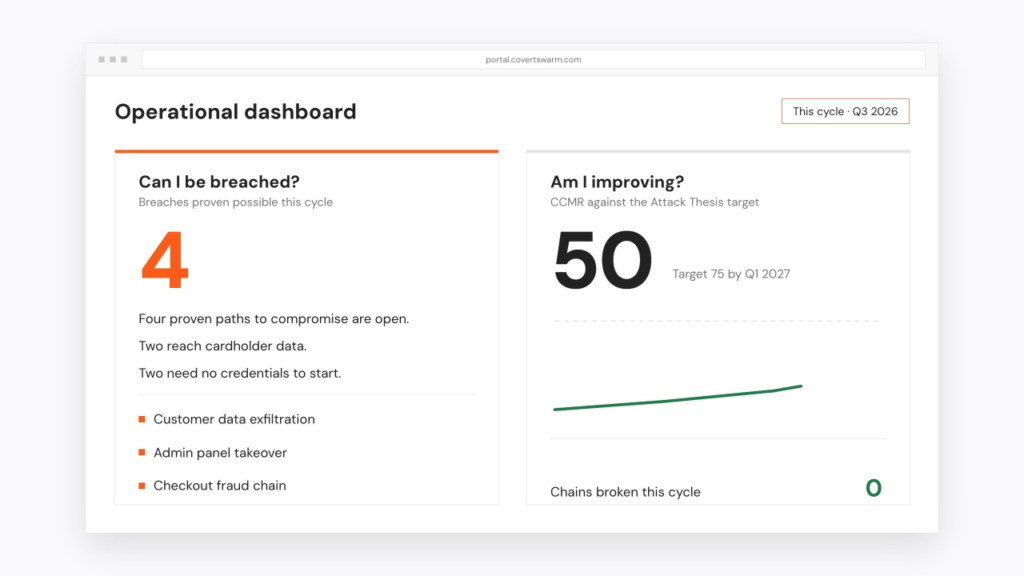
Your direct line to the Swarm.
See what your Swarm is targeting, what they have proven and what needs fixing. One shared view of the attacks and your response, all in the CovertSwarm portal.
What your first year looks like
We hit hard from the start. Then keep finding ways to push further.
Today
Day zero.
Get an attacker’s external view of your organization before you subscribe.
An attacker’s view of your risks
A read on your cyber maturity
Quick wins to act on now
A first Attack Thesis
Your subscription starts
Day one.
Human and agentic attacks against priority targets, to set your current risk baseline.
Meet your Swarm
Agree rules and priorities
Human + agentic attacks
Act on clear, actionable findings
Day 90
Day 90.
Get board-ready proof of your current state, and a 12-month plan built on attacker objectives.
Board-ready attack evidence
Know what needs investment
Comprehensive Attack Thesis
12-month Attack Plan
Ongoing
Ongoing.
Continuous and evolving attack campaigns across digital, social and physical channels.
Continuous attack cycles
A persistent, creative attacker
Unlimited access to the Swarm
Compliance testing built in
The value of your subscription compounds over time.
Attackers that are always learning
Every cycle, the Swarm learns more about you. Every attack is stronger, more focused and more capable.
Proof that stacks up
Build a growing record of what held and what broke, cycle after cycle, board-ready and audit-ready.
A battle-tested team
Your people face complex, real attacks. The more we find together, the faster you fix, until it becomes routine.
Get an attacker’s view of your business at no cost.
Schedule a conversation with an expert attacker to see your organization the way an attacker will.
You’ll receive your Cyber Risk Gap report at no cost, and where the next attack could start.
Pricing
A subscription that helps you outpace changing threats and stay ahead of your real risk.
Starting at $10,995/month
An APT built for you that keeps constant pressure on your whole organization
Digital, social and physical attacks. No fixed scopes. No change orders.
Human-led attacks, augmented by agentic tools
Board-ready evidence of what’s working and what needs attention
Each attack leaves your team sharper and more resilient
No access to your systems required.
What CovertSwarm replaces
CovertSwarm combines multiple security programs under one simple subscription. Less to buy and to manage. More time to focus.
| Option | What it covers | Methodologies | Shelf life | What you get |
|---|---|---|---|---|
| Penetration test | Selected systems | Digital | Until the report | A PDF |
| Red team | An agreed scope | Fixed playbook | Until the report | A PDF |
| Bug bounty | Your perimeter | Scoped applications | While it’s live | Platform findings |
| AI testing platform | Systems it can reach | Digital | Until the next scan | Platform findings |
| CovertSwarm subscription | Your organization | Social, digital, physical | Always current | Board-ready evidence |
Not ready for a subscription yet? Explore one-off engagements
Use Cases
Your biggest security problems each have an attacker behind them. Constant Cyber Attack™ becomes that attacker, so you can see what holds and what to fix.
-
Regulatory and compliance readiness
Compliance is mandatory. Attackers are relentless. Get threat-led, regulator-aligned testing while strengthening real-world resilience.
-
Prove the effectiveness of your security investments
You’ve invested in security. Now demand proof it works. CovertSwarm attacks your technology, people and processes to reveal what stops an adversary, what fails and where to focus next.
-
Secure your AI and agentic systems
CovertSwarm attacks your agents and AI apps to show how attackers could breach them, and what they could reach.
-
Improve resilience against AI-enabled attacks
CovertSwarm prepares you to meet the pace and intensity of AI-enabled attackers.
-
Unknown risk discovery
CovertSwarm strengthens your security posture by continuously attacking, exposing, and mapping currently unknown risks.
Stories from the Swarm
These stories are real, but the names are redacted. Discover how we uncovered the paths no one else could see, and why constant cyber attack is the best way to outpace cyber threats.
Become a story well told. Contact us to discuss how Constant Cyber Attack will help you outpace cyber threats.
Stop testing.
Start knowing.
You’ll know exactly where you stand, and you’ll be able to prove it. To your board, your regulator, and yourself.
Transform to a proactive, continuous offensive security program
Your budget is aimed at the risk that matters, not the one you were handed
You show the board what security prevented, not a request for more
Security clears the way for the business to move faster
You enter the boardroom in command
It starts with a 30-minute Attack Discovery call.
No access to your systems required.