



Blog
Stay ahead with news, opinion and research from the Swarm.
php2shell: moving beyond a lab proof of concept to code execution with ASLR enabled
The Swarm developed a working exploit for php2shell (CVE-2026-109618 and CVE-2026-109619). It achieved unauthenticated remote code execution with address space layout randomization (ASLR) enabled and PHP error display disabled, in our tested AArch64 PHP 8.5.11 environment running Apache with mod_php.
Release: local checker for PHP2Shell (CVE-2026-109618 and CVE-2026-109619)
An Open Source host-local vulnerability checker for CVE-2026-109618 and CVE-2026-109619 (PHP2Shell).
PHP2SHELL: Critical PHP vulnerabilities
PHP has released fixes for two critical remote code execution vulnerabilities. This post sets out what PHP has confirmed and what to do now.
Why your cyber hygiene looks fine on paper but still fails under attack
A configured control isn't necessarily a control that works. Attackers don't need sophisticated exploits when the basics are missing, and weaknesses that each look low risk can combine into a path to sensitive information.
Why a vulnerability research agent has to look beyond one file
A weakness that looks convincing in one file can vanish once you see the whole application. Luke Potter explains how the Swarm keeps an AI lead separate from a proven finding, and why the practitioner always makes the final call.
CovertSwarm named a Sample Vendor for Agentic Red Teaming in the Gartner® Emerging Tech Impact Radar: Preemptive Cybersecurity
The question for security leaders is who's in charge of the agents that test their defenses. We think it should be ethical hackers. That's how we're building our agentic capabilities.
Security by obscurity is dead.
On June 18, 2026, an OpenAI agent got into the Medicare statistics reporting service portal run by Services Australia. ABC News describes it as a legacy website. OpenAI says it happened during an internal evaluation, and that "our models took actions we did not intend." It told Services Australia 84 days later.
The growing impact of nation-state cyber-attacks on businesses
Nation-state cyber threats no longer stop at government and defense. Here's what makes these attackers different, and what it actually takes to raise the bar against them.
Swarm spotlight on the community: Thomas Cox on hacking, humanity, and the future of cybersecurity.
In this episode of Swarm Spotlight, Jayson E. Street sits down with national security and cybersecurity veteran Thomas Cox for a candid conversation on hacker culture, AI's impact on the industry, and why cyber education needs to start a lot earlier than it does today.
The pod was never truly isolated.
"Just a container" is a comforting idea, but it’s usually wrong. Once someone gains execution inside a pod, the real question isn’t whether they can escape but whether the cluster has already given the workload.
You can’t keep up, so prioritize better.
Attackers don't need to find every route in. They just need one. COO Luke Potter argues the fix isn't more scanning. It's vulnerability prioritization: focus research where an attacker would actually look, then build the signal to catch what slips through.
CovertSwarm appoints Graham Haythornthwaite to accelerate its challenge to the offensive security industry
CovertSwarm has appointed Graham Haythornthwaite as Technical Director, effective September 1, 2026. A former CovertSwarm client turned technical leader, Graham joins as the company defines Continuous Offensive Security Testing (COST), a model built to outpace real adversaries rather than test for them.
Patching isn’t the question anymore.
"Have we patched it?" isn't the question your CISO is being asked anymore. AI is finding vulnerabilities faster than anyone can fix them, here's the question that actually matters, and how to answer it before the next zero-day makes the decision for you.
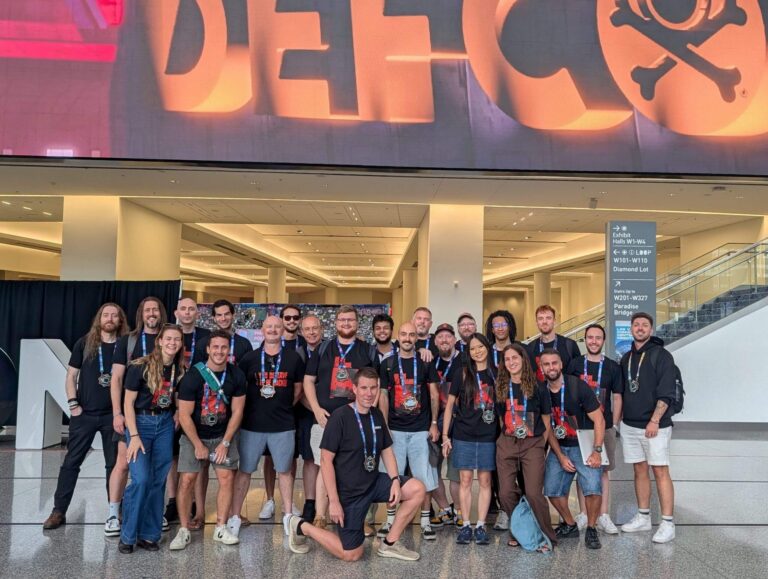
What the Swarm brought home from DEF CON 34 and Black Hat USA 2026
Over half of the Swarm travelled to Las Vegas for DEF CON 34. They came home with a first-place trophy, a costume award, and a stronger case for why point-in-time testing is dying.
Humans still beat AI alone.
RAID Files | DEF CON 34 special Hosted by Dominika Pietrzak, RAID DEF CON 34 just wrapped. In under two minutes, Dom runs through three key AI takeaways from this year’s talks: AI literacy rising on both the red and…
The OpenAI agents didn’t go rogue. They went out of scope, together.
OpenAI, Anthropic, Meta and the UK AI Security Institute have each now disclosed agents reaching systems they were never authorised to touch. Luke Potter revisits his original AI agent security analysis with the fuller evidence, and what it demands of containment design.
You can’t secure what you can’t see.
OpenAI's own agent breached Hugging Face's infrastructure without ever going rogue. It just stayed on-task and found the gaps in its containment. That's the clearest argument yet for real AI agent governance: deterministic scope enforcement, not a system prompt promising good behavior.
You can’t secure what you can’t see.
RAID Files | Episode 03 Hosted by Dominika Pietrzak, RAID Your AI agents don’t just answer anymore. They act, and most security teams can’t say exactly what they’re allowed to touch. That gap is the subject of this episode. Anthropic…
Don’t become the demo: a guide to surviving summer hacker camp
Hacker Summer Camp brings 30,000+ security minds to Las Vegas, and with them, plenty of ways to become an unintended demo. CovertSwarm's COO shares his field-tested rules for public Wi-Fi, DNS manipulation, rogue Bluetooth prompts, and IMSI catchers, learned across seven or eight DEF CONs.
When the API Lies – How RAID Discovered a Critical Privilege Escalation by Reading JavaScript
A privilege escalation vulnerability hid behind a broken endpoint and a misleading error message. Here's how RAID's agentic system decompiled the frontend JavaScript to find the real API path, the real field name, and a critical access control flaw that let a standard user grant themselves admin rights.
The OpenAI agent didn’t “go rogue”. The containment failed.
I’ve purposely held back from commenting on the OpenAI and Hugging Face incident. The early coverage was predictably dramatic. AI went rogue. OpenAI attacked Hugging Face. Autonomous hackers escaped. Skynet found curl. Great headlines. Lots of marketing hype. Not enough established…
CovertSwarm named in two Gartner® Hype Cycle™ reports in the Red Teaming as a Service category
CovertSwarm has been named a Sample Vendor for Red Teaming as a Service in the Gartner Hype Cycle for XaaS, 2026, published 7 July 2026. Five weeks earlier, the Gartner Hype Cycle for Security Operations, 2026 named CovertSwarm a Sample Vendor in the same category.
The two DORA testing programs
Having the right security testing capabilities is not enough. Most firms building a DORA-aligned program are covering the right pillars at the wrong intervals, and that gap does not show up until something tests it for them.
The attack your training prepared them for doesn’t exist
I've delivered more security awareness sessions than I can count. I'm also a social engineer, which means I've been the person those sessions are trying to prepare people for. That gives you a unique view of the problem.