Swarm Intelligence
A weakness that looks convincing in one file can vanish once you see the whole application. Luke Potter explains how the Swarm keeps an AI lead separate from a proven finding, and why the practitioner always makes the final call.
Why a vulnerability research agent has to look beyond one file
A weakness that looks convincing in one file can vanish once you see the whole application. Luke Potter explains how…
When the API Lies – How RAID Discovered a Critical Privilege Escalation by Reading JavaScript
A privilege escalation vulnerability hid behind a broken endpoint and a misleading error message. Here's how RAID's agentic system decompiled…
How RAID found unauthenticated customer data in a retail GraphQL API
CovertSwarm's web testing agent identified a critical broken access control vulnerability in a retail subscription platform's GraphQL middleware. The platform…
When “Just Logging In” Isn’t Just Logging In: A look at xrdp and CVE-2026-33145
A quiet finding with real-world impact. CVE-2026-33145 shows how xrdp's AlternateShell feature, enabled by default, passes client-supplied input directly into…
Project Glasswing is impressive. But what about the rest?
Anthropic's Project Glasswing is a serious step forward for technical security. But it covers one third of the attack surface.…
Swarm Intelligence: Stryker’s Intune wipe proves your BCDR plan has a single point of failure
No malware. No ransomware. One compromised Global Admin account and the management console your IT team used this morning. The…
Claude Jailbroken To Attack Mexican Government Agencies
A threat actor jailbroke Claude to orchestrate a month-long attack on Mexican government networks, stealing 150 GB of sensitive data.…
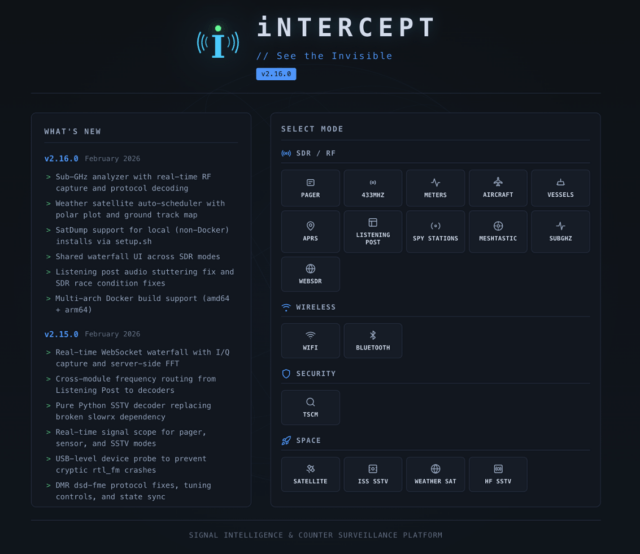
iNTERCEPT – How A Small RF Experiment Turned Into A Community SIGINT Platform
I've always been fascinated by RF. There's something about the fact that it's invisible, the fact that you might be…
When Your IDE Becomes An Insider: Testing Agentic Dev Tools Against Indirect Prompt Injection
Agentic development tools don't need to bypass your firewall. They're already inside. And if an attacker can control what they…