




Swarm Director
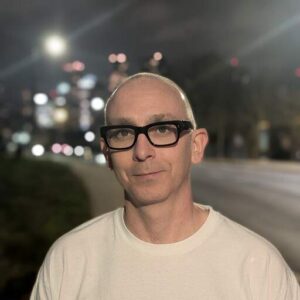
James Dale
About James
James Dale has spent over two decades operating at the sharp end of enterprise cybersecurity. His specialism is adversary simulation: understanding how real threat actors think, how they move through complex environments, and how organizations can be made genuinely resilient against them. Not just compliant. Resilient.
He joined CovertSwarm in January 2025 as Head of Adversary Simulation and Regulatory Testing, bringing with him a career built on leading sophisticated red team engagements for some of the most security-conscious organizations globally, with particular depth in the financial services sector. That background matters. Banks, insurers, and payment infrastructure providers face threat actors that are well-resourced, patient, and not limited by scope. Testing against that kind of adversary requires a different calibre of operator.
James is a CREST Fellow, a distinction awarded to those who have demonstrated exceptional contribution to the profession over sustained periods. His elite certifications include CCRTS (CREST Certified Red Team Specialist) and CCSAM (CREST Certified Simulated Attack Manager), placing him among a small number of practitioners qualified to lead the most demanding threat-led engagements the UK financial services sector requires.
At CovertSwarm, James leads the regulatory testing practice, overseeing CBEST and STAR-FS engagements for clients in regulated industries. When CovertSwarm achieved its CBEST accreditation in March 2025, James framed it plainly: “CBEST represents the pinnacle of regulatory security testing in our industry.” His approach to all testing reflects the same clarity. The question is never whether a vulnerability exists. The question is whether an attacker already inside your environment would be noticed.
Latest posts
Mythos found a $20,000 bug. It won’t tell you who’s already inside.
Anthropic's Mythos has dominated the security conversation this week, but the debate about whether it's overhyped is the wrong argument. The real question is simpler and more uncomfortable: if an attacker had execution inside your environment right now, would you know?
Proving Resilience: The Role of Regulator-Led Testing in Strengthening Market Stability.
Red teaming in regulated environments has become essential for organisations facing sophisticated cyber threats. While traditional penetration tests provide value, red teaming goes further – simulating realistic adversary behaviour to test defences under real-world conditions. For UK financial services, this…
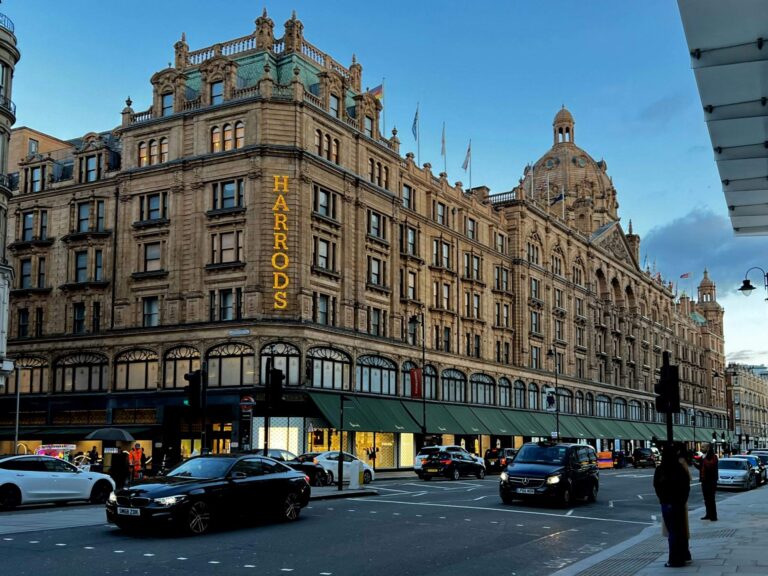
Retail Under Siege: The Coordinated Cyber Assault on UK’s Top Stores
With Marks & Spencer, Co-op, and Harrods all experiencing significant security incidents within a short timeframe, the pattern suggests a coordinated campaign that demanded immediate attention from security leaders across all retail operations.that demanded immediate attention from security leaders across all retail operations.