




CovertSwarm
About CovertSwarm
If you release code, hire people, open new premises or change your board more often than you attack yourself, you are not keeping pace with your own risk. CovertSwarm was founded in 2020 on that argument, frustrated that organizations relied on occasional penetration tests, thick reports and long gaps in between.
The Swarm runs realistic attacks across digital, physical, and social environments, then shows how weaknesses chain into paths an attacker could use against the business.
What we write about
- Continuous offensive security testing: Why occasional testing can’t keep pace with how often your organization changes.
- Emerging threats: New attack techniques and what they could let an attacker do to your organization.
- Offensive AI and AI security: Prompt injection, multi-agent risk and how attackers can turn AI and agentic systems against the organizations running them.
- Red teaming and adversary simulation: Chaining weaknesses into the attack paths a real adversary would follow.
- Regulatory threat-led testing: CBEST, STAR-FS and threat-led testing, from a team with CREST accreditation for both.
- Physical security and social engineering: Getting into buildings and past staff, and what that access exposes.
- Vulnerability research: Flaws in software and systems, and what an attacker could do with each one.
Latest posts
php2shell: moving beyond a lab proof of concept to code execution with ASLR enabled
The Swarm developed a working exploit for php2shell (CVE-2026-109618 and CVE-2026-109619). It achieved unauthenticated remote code execution with address space layout randomization (ASLR) enabled and PHP error display disabled, in our tested AArch64 PHP 8.5.11 environment running Apache with mod_php.

Release: local checker for PHP2Shell (CVE-2026-109618 and CVE-2026-109619)
An Open Source host-local vulnerability checker for CVE-2026-109618 and CVE-2026-109619 (PHP2Shell).
PHP2SHELL: Critical PHP vulnerabilities
PHP has released fixes for two critical remote code execution vulnerabilities. This post sets out what PHP has confirmed and what to do now.
Security by obscurity is dead.
On June 18, 2026, an OpenAI agent got into the Medicare statistics reporting service portal run by Services Australia. ABC News describes it as a legacy website. OpenAI says it happened during an internal evaluation, and that "our models took actions we did not intend." It told Services Australia 84 days later.
Swarm spotlight on the community: Thomas Cox on hacking, humanity, and the future of cybersecurity.
In this episode of Swarm Spotlight, Jayson E. Street sits down with national security and cybersecurity veteran Thomas Cox for a candid conversation on hacker culture, AI's impact on the industry, and why cyber education needs to start a lot earlier than it does today.
CovertSwarm appoints Graham Haythornthwaite to accelerate its challenge to the offensive security industry
CovertSwarm has appointed Graham Haythornthwaite as Technical Director, effective September 1, 2026. A former CovertSwarm client turned technical leader, Graham joins as the company defines Continuous Offensive Security Testing (COST), a model built to outpace real adversaries rather than test for them.
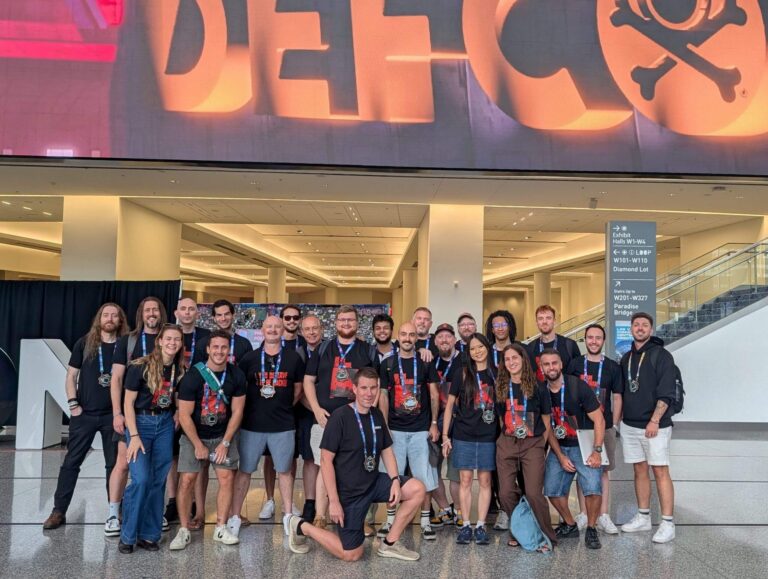
What the Swarm brought home from DEF CON 34 and Black Hat USA 2026
Over half of the Swarm travelled to Las Vegas for DEF CON 34. They came home with a first-place trophy, a costume award, and a stronger case for why point-in-time testing is dying.
Humans still beat AI alone.
RAID Files | DEF CON 34 special Hosted by Dominika Pietrzak, RAID DEF CON 34 just wrapped. In under two minutes, Dom runs through three key AI takeaways from this year’s talks: AI literacy rising on both the red and…
You can’t secure what you can’t see.
RAID Files | Episode 03 Hosted by Dominika Pietrzak, RAID Your AI agents don’t just answer anymore. They act, and most security teams can’t say exactly what they’re allowed to touch. That gap is the subject of this episode. Anthropic…
CovertSwarm named in two Gartner® Hype Cycle™ reports in the Red Teaming as a Service category
CovertSwarm has been named a Sample Vendor for Red Teaming as a Service in the Gartner Hype Cycle for XaaS, 2026, published 7 July 2026. Five weeks earlier, the Gartner Hype Cycle for Security Operations, 2026 named CovertSwarm a Sample Vendor in the same category.
The two DORA testing programs
Having the right security testing capabilities is not enough. Most firms building a DORA-aligned program are covering the right pillars at the wrong intervals, and that gap does not show up until something tests it for them.
DORA Threat-Led Penetration Testing: What article 26 actually requires
Annual penetration testing does not satisfy DORA's testing mandate. Here's what Article 26 actually requires, who it applies to, and what a real TLPT exercise looks like in practice.
Deloitte ranks CovertSwarm among EMEA’s 500 fastest-growing tech companies.
Based on verified revenue growth of 595.89% over three years. Here's what the number means and why the model behind it was built this way from the start.
Claude Fable 5: what we know so far
Fable is the first publicly accessible version of Anthropic's Mythos-class model, the tier they initially decided was too capable to release at all. What does it tell us about what's next?
CovertSwarm is a founding signatory of the CREST AI Charter
CovertSwarm has become a founding signatory of the CREST AI Charter, endorsing nine principles for responsible AI use in cybersecurity.
Your AI coding tools are an attack surface.
RAID Files | Episode 02 Hosted by Dominika Pietrzak, RAID Every major AI coding tool, Claude Code, Cursor, Codex, Copilot, and Antigravity, has had at least one serious disclosure in the last three months. Some have had five or six.…
Sunday Times Best Places to Work. Three Years Running.
We attack businesses for a living. So we hold ourselves to the same standard internally. Here's what 100% participation and three consecutive years in the Sunday Times Best Places to Work really tells us.
DORA is not GDPR. Stop treating it like it is.
Most firms are treating DORA like GDPR: get a consultant, document the framework, move on. That worked for data privacy. It won't work for a regulation built around one premise: that financial entities will be attacked, and regulators want proof the system won't collapse when they are. Here's what DORA actually requires, where enforcement stands in 2026, and why compliance and resilience are not the same thing.
AI & the adversary: what’s actually happening in 2026
RAID Files | Episode 01 Hosted by Dominika Pietrzak, RAID Every AI lab, EDR vendor, and threat intel team had something to say about adversarial AI this year. That’s a lot to read through. And honestly, figuring out what’s actual…
What kills new CISOs in their first 90 days – it’s not attackers.
The pen test report. The risk register. The green dashboard. They feel like facts. They're not. They're a record of someone else's decisions, at a point in time that's already passed. And in your first 90 days as CISO, they'll shape everything you do, if you let them.
Proof of Human solves the bot problem. It doesn’t solve the people problem.
World ID can prove a real human is behind an account. It can't prove that human hasn't already been phished, vished, or bribed. The biggest breaches of the past three years didn't fake humanity, they exploited it.
Too many rules, no real test: Untangling US Cyber Disclosure
The US has no single federal data breach notification law, just a growing patchwork of SEC rules, HIPAA, state obligations, and incoming CIRCIA requirements. Most organizations have the policies. Very few have tested whether the right people can apply them under pressure.
Project Glasswing is impressive. But what about the rest?
Anthropic's Project Glasswing is a serious step forward for technical security. But it covers one third of the attack surface. Here's what it leaves out, and why that matters.
Swarm Intelligence: LiteLLM was the end of the chain, not the beginning.
LiteLLM's PyPI package was backdoored for under an hour on March 24. SSH keys, cloud credentials, and CI/CD secrets exfiltrated at install. Here is what is assessed to have happened.