




CovertSwarm
About CovertSwarm
If you release code, hire people, open new premises or change your board more often than you attack yourself, you are not keeping pace with your own risk. CovertSwarm was founded in 2020 on that argument, frustrated that organizations relied on occasional penetration tests, thick reports and long gaps in between.
The Swarm runs realistic attacks across digital, physical, and social environments, then shows how weaknesses chain into paths an attacker could use against the business.
What we write about
- Continuous offensive security testing: Why occasional testing can’t keep pace with how often your organization changes.
- Emerging threats: New attack techniques and what they could let an attacker do to your organization.
- Offensive AI and AI security: Prompt injection, multi-agent risk and how attackers can turn AI and agentic systems against the organizations running them.
- Red teaming and adversary simulation: Chaining weaknesses into the attack paths a real adversary would follow.
- Regulatory threat-led testing: CBEST, STAR-FS and threat-led testing, from a team with CREST accreditation for both.
- Physical security and social engineering: Getting into buildings and past staff, and what that access exposes.
- Vulnerability research: Flaws in software and systems, and what an attacker could do with each one.
Latest posts
One Hive Member’s insights into how and why our industry should change
CovertSwarm is an offensive security pioneer. Our research, tests and assaults continuously probe your attack surface to identify weaknesses and help you fix them in real-time for cyber security that never sleeps. This continuous testing approach is unique in our…

We’re Security Current’s 2022 CISO Choice Awards Finalists!
The Security Current CISO Choice Awards™ 2022 returns this year, recognising the security leaders in key technology and business categories.
FortiOS / FortiProxy / FortiSwitchManager – Authentication Bypass (CVE-2022-40684)
We would like to bring to your attention a newly discovered authentication bypass vulnerability within FortiOS, FortiProxy and FortiSwitchManager. This vulnerability is currently being actively exploited. An authentication bypass has been identified using an alternate path or channel vulnerability [CWE-288]…
Critical Zero-Day Vulnerability in Microsoft Exchange
CVE-2022-41040, CVE-2022-41082, ZDI-CAN-18333, ZDI-CAN-18802 We would like to update you on the following critical 0-day vulnerability in Exchange Server. While this issue is being exploited in the wild, the scope of these attacks is currently unknown. A previously unknown authenticated…
CovertSwarm: How our technology helps you
At CovertSwarm our mission is to constantly compromise our clients.
Unauthenticated Remote Code Execution in Magento 2 and Adobe Commerce Systems (CVE-2022-24086)
A unauthenticated remote code-execution (RCE) bug in the Magento 2 and Adobe Commerce platforms was originally discovered in February 2022.
Pentest from your pocket with Flipper Zero
We’re CovertSwarm – expert ethical hackers, red teamers and penetration testers. From testing out new tech for our clients, to networking and competing at events like DEF CON, we work relentlessly to sharpen our skills and give back to the cyber community.
Critical vulnerability identified in WordPress plugin “BackupBuddy” (CVE-2022-31474)
We would like to bring to your attention a newly discovered vulnerability within the WordPress plugin “BackupBuddy".
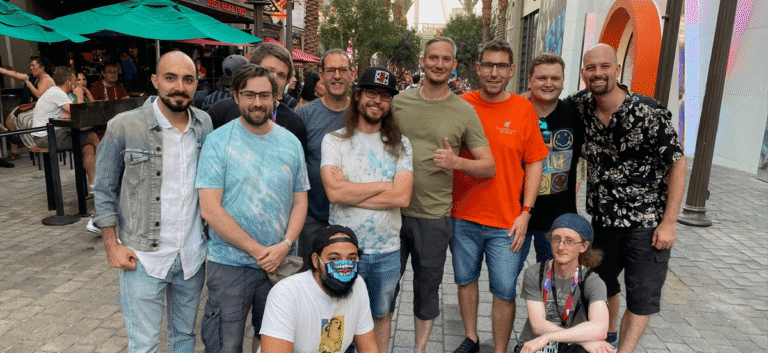
DEF CON 30: what we learned (and how it helps you)
In August, the CovertSwarm team attended DEF CON 30 in Las Vegas – the cyber industry’s premier hacker convention, and the oldest and largest of its kind.
Working at CovertSwarm: Our First Intern
Being part of the cyber security community and shaping it for the better is really important to CovertSwarm. Not only do we actively share our knowledge and experience, but we network with experts in a range of specialisms, and only…
Critical RCE in DrayTek Routers (CVE-2022-32548)
We would like to bring your attention to the following critical remote code execution vulnerability we have recently become aware of which affects the following DrayTek products: The vulnerability allows remote unauthenticated attackers to execute commands on the affected routers…
Why a cyber value proposition should be part of your business strategy
Whatever your industry, it’s critical to think about your cyber security posture in the right way.
Critical vulnerabilities identified in VMware products (CVE-2022-31656)
We would like to bring your attention to the following critical vulnerabilities we have recently become aware of which affects the following VMware products: VMware is urging all users of the above applications to apply the latest patches in order…
DEF CON 30: what it is and where to find us
When it comes to your cyber security, you have to keep ahead of the curve.
Exploiting Microsoft Windows 11 via Process No-Hollowing
An adapted technique to bypass Managed Detection and Response (MDR) and Endpoint Detection and Response (EDR) solutions.
Working at CovertSwarm: One Hive Member’s Experience
Jack Smith is a Cyber Security Consultant and Red Team Hive Member and one of our newest additions to the Swarm. Over the past 8 months Jack has proved invaluable, with his cyber security skills matched only by his passion for the industry.
Constant offensive security – How does it all work?
Luke Potter, CovertSwarm’s COO, explains everything you need to know about our continuous approach to offensive security. Contact us to learn more about how we support organizations around the world to increase their security posture and outpace cyber threats.
The Tiber EU Framework: What is it and why is it important?
At CovertSwarm, we’re a proud part of the cyber security sector and nothing slips under our radar. In fact, from the latest technology to best-practice testing methods, our Swarm rallies to keep our knowledge base growing, our clients better protected…
Zero-day vulnerability in Atlassian Confluence
We would like to bring to your attention the recently discovered unauthenticated remote code execution vulnerability in Atlassian Confluence (CVE-2022-26134). Description Confluence Server and Data Center editions are affected by the unauthenticated remote code execution flaw and are currently under…
The Internet of Things: Securing the Hidden Attack Surface of Your Home
Almost a quarter (23%) of Britons have at least one smart home device (YouGov), and global revenue for the sector is predicted to hit $9bn this year (Statista). It’s tempting to think that a password or two might be all…
Zero-day vulnerability in Microsoft Office – Follina
We would like to bring your attention to the following 0-day exploit we have recently become aware of. Follina – A zero-day Microsoft Office code execution vulnerability that bypasses Microsoft Defender for Endpoint. This vulnerability has been seen to be…
Diary of a Cyber Attacker
When you think of an attacker, it’s tempting to imagine a Matrix-style hacker in a hoodie. In reality, these bad actors are highly intelligent experts in the cyber landscape — and they’re at the top of their game.
CovertSwarm Inc. launched in North America
CovertSwarm has modernized the cyber security industry through its Constant Cyber Attack™ subscription service and Offensive Operations Center attack platform. Today, they announce the brand’s expansion into the North American market as delivery of a major strategic milestone in their mission to outpace their client's genuine cyber threats.
CovertSwarm supports BBC to advise social media account hijack victims
CovertSwarm has modernised the cyber security industry with its challenger ‘Constant Cyber Attack’ subscription service. Today, they announce their latest collaboration with the BBC to provide insights and guidance to combat the hijacking of user accounts upon popular social media platforms such as Twitter and Instagram.