




CovertSwarm
About CovertSwarm
If you release code, hire people, open new premises or change your board more often than you attack yourself, you are not keeping pace with your own risk. CovertSwarm was founded in 2020 on that argument, frustrated that organizations relied on occasional penetration tests, thick reports and long gaps in between.
The Swarm runs realistic attacks across digital, physical, and social environments, then shows how weaknesses chain into paths an attacker could use against the business.
What we write about
- Continuous offensive security testing: Why occasional testing can’t keep pace with how often your organization changes.
- Emerging threats: New attack techniques and what they could let an attacker do to your organization.
- Offensive AI and AI security: Prompt injection, multi-agent risk and how attackers can turn AI and agentic systems against the organizations running them.
- Red teaming and adversary simulation: Chaining weaknesses into the attack paths a real adversary would follow.
- Regulatory threat-led testing: CBEST, STAR-FS and threat-led testing, from a team with CREST accreditation for both.
- Physical security and social engineering: Getting into buildings and past staff, and what that access exposes.
- Vulnerability research: Flaws in software and systems, and what an attacker could do with each one.
Latest posts
What is API testing?
Read our guide to find out what API tests are, how they work, why they’re important, best practices & some commonly asked questions.

What is email spoofing?
Read our complete guide to find out what email spoofing is, how it works, why it’s dangerous & how to identify, defend against & prevent it.
What is an IDS (Intrusion detection system)?
Read our guide on intrusion detection systems to find out what they are, why they’re important, challenges & considerations & lots more.
Vishing: everything you need to know
Read our guide to find out what vishing is, how it works, why it exists & how to identify, respond to, recover from & prevent it.
What is Kerberos authentication?
Read our guide on Kerberos authentication, including what it is, how it works, why organizations need it & some commonly asked questions.
What Does SDLC Mean?
Read our blog to find out what the Software Development Life Cycle (SDLC) is, its benefits for organizations & different methodologies.
CovertSwarm Named Top UK Cybersecurity Firm by TechRound
The leading tech publisher recently released its inaugural Cybersecurity40 winners, celebrating the most innovative cybersecurity companies and initiatives across the UK and Europe.
The trials and tribulations of secure software development
Discover effective strategies for managing third-party libraries, tackling security challenges & handling technical debt in secure software development.
CovertSwarm launches in-house Academy Program
Socially-focused initiative has been designed to make a career in cybersecurity more accessible than ever before
What is endpoint security and why is it important?
Read our guide to find out what endpoint security is, how it works, why it’s important for organizations and some best practices.
What is Cross-Site Scripting (XSS) and how do you prevent it?
Read our guide to find out what Cross Site Scripting (XSS) is, how it works, why it’s dangerous and how to detect, recover from and prevent it.
Multi-Factor Authentication (MFA): what you need to know
Read our blog to find out what Multi-Factor Authentication (MFA) is, why it’s vital to have it and how AI makes it more secure & efficient.
What are brute force attacks?
Read our blog to find out what brute force attacks are, how they work, why they’re dangerous and how to identify, recover from and prevent them.
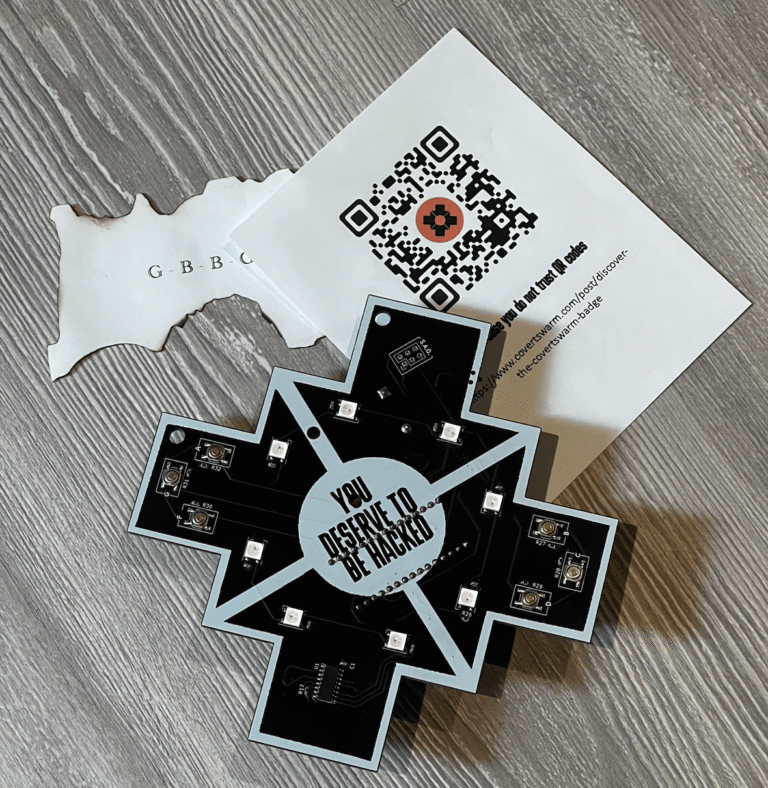
We’re joining the Badge Life Movement: Discover the CovertSwarm Badge at DEF CON 31
Will the CovertSwarm Badge will be joining your Badge Life collection at DEF CON 31?
CovertSwarm secures investment from beech tree private equity
Beech Tree Private Equity announces an investment in CovertSwarm, a leading red team-as-a-service and cyber-attack simulation platform.
What is an eavesdropping attack?
Read our guide to find out about what eavesdropping attacks are, why they exist, their objectives and how to prevent them.
What is DNS and how does it work?
Read our guide to find out what DNS is, how it works, what attacks they can be prone to and security measures to carry out.
What is smishing and how do you prevent it?
Read our guide to find out what smishing is, different types, why it’s a problem for organizations and how to prevent it.
What is spear phishing and how do you prevent it?
Read our guide to find out what spear phishing is, why it’s a problem for organizations and how to prevent it.
CovertSwarm revolutionizes Attack Surface Management with launch of free CovertSwarm Portal
Our new platform is the missing link that joins SaaS-identified vulnerabilities and the ability to validate risk through a seamless ‘one click’ submission for ethical hacker testing.
Why red team exercises should be included in your company’s supply chain defense strategy
Supply chain attacks are a threat to companies and end users. Read this blog to find out why red teams need to be a part of your defense strategy.
SteelCon 2023: diary of a conference goon
Earlier this month, one of our Swarm members volunteered at one of the most prestigious hacker conferences in the UK, SteelCon.
What is a SQL injection (SQLi) attack and how can you prevent them?
SQL injection is a complex world, but it’s important for organizations to understand the impact and preventative measures. Read our guide.
What is malware and how can you prevent it?
Read our guide to find out what malware is, why it exists, different types and how to prevent it to keep your organization safe.