



Blog
Stay ahead with news, opinion and research from the Swarm.
Simplify your vulnerability management workflow in Jira
Atlassian's Jira is an extremely popular platform for managing not only product development but workloads of different kinds within an organization.
Introducing Will Morrish, CovertSwarm Chief Revenue Officer
We’re kicking off 2023 with an in-depth interview and with our Chief Revenue Officer, Will Morrish – the newest member of CovertSwarm’s leadership team. In our accompanying podcast, Will shares his passions for cyber security and technology, his career up until now, and what’s exciting him most about joining the Swarm.
What is password cracking and how does it work?
Read our blog to find out what password cracking is, some common tactics that hackers use to do it & how you can avoid it.
Enhance team cyber collaboration with our new Slack integration
Over its lifetime the CovertSwarm Portal has had many revisions and improvements to how organizations and users interact with the portal.
Citrix Gateway and Citrix ADC Security Bulletin for CVE-2022-27510 CVE-2022-27513 and CVE-2022-27516
Threat alert details We would like to bring your attention to a recent security bulletin surrounding Citrix Gateway and Citrix ADC. Vulnerabilities have been discovered in Citrix Gateway and Citrix ADC, listed below. Note that only appliances that are operating…
Discovering and identifying change to your organization’s attack surface
The CovertSwarm Portal is a gateway to understanding the exposure of your organization and the risks that may present themselves over time. Gaining that initial understanding of what is out there is crucial in every initial step, both from an attack and defense perspective.
Winners of the CISO Choice Awards ‘Breach & Attack Simulation Service Provider’
We are proud to announce that CovertSwarm has won the Breach & Attack Simulation Service Provider category at the 2022 CISO Choice Awards.
One Hive Member’s insights into how and why our industry should change
CovertSwarm is an offensive security pioneer. Our research, tests and assaults continuously probe your attack surface to identify weaknesses and help you fix them in real-time for cyber security that never sleeps. This continuous testing approach is unique in our…
We’re Security Current’s 2022 CISO Choice Awards Finalists!
The Security Current CISO Choice Awards™ 2022 returns this year, recognising the security leaders in key technology and business categories.
FortiOS / FortiProxy / FortiSwitchManager – Authentication Bypass (CVE-2022-40684)
We would like to bring to your attention a newly discovered authentication bypass vulnerability within FortiOS, FortiProxy and FortiSwitchManager. This vulnerability is currently being actively exploited. An authentication bypass has been identified using an alternate path or channel vulnerability [CWE-288]…
Critical Zero-Day Vulnerability in Microsoft Exchange
CVE-2022-41040, CVE-2022-41082, ZDI-CAN-18333, ZDI-CAN-18802 We would like to update you on the following critical 0-day vulnerability in Exchange Server. While this issue is being exploited in the wild, the scope of these attacks is currently unknown. A previously unknown authenticated…
CovertSwarm: How our technology helps you
At CovertSwarm our mission is to constantly compromise our clients.
Unauthenticated Remote Code Execution in Magento 2 and Adobe Commerce Systems (CVE-2022-24086)
A unauthenticated remote code-execution (RCE) bug in the Magento 2 and Adobe Commerce platforms was originally discovered in February 2022.
Pentest from your pocket with Flipper Zero
We’re CovertSwarm – expert ethical hackers, red teamers and penetration testers. From testing out new tech for our clients, to networking and competing at events like DEF CON, we work relentlessly to sharpen our skills and give back to the cyber community.
Critical vulnerability identified in WordPress plugin “BackupBuddy” (CVE-2022-31474)
We would like to bring to your attention a newly discovered vulnerability within the WordPress plugin “BackupBuddy".
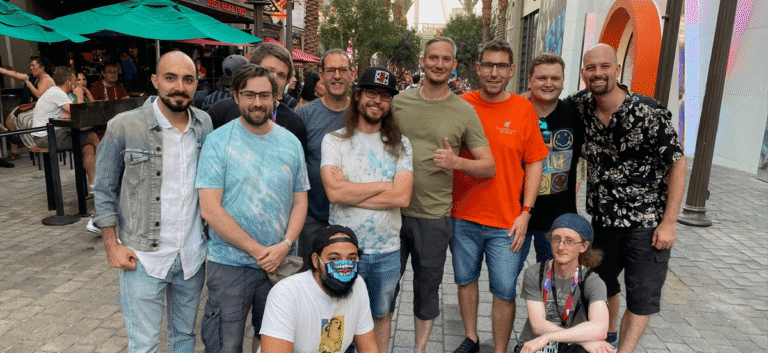
DEF CON 30: what we learned (and how it helps you)
In August, the CovertSwarm team attended DEF CON 30 in Las Vegas – the cyber industry’s premier hacker convention, and the oldest and largest of its kind.
Working at CovertSwarm: Our First Intern
Being part of the cyber security community and shaping it for the better is really important to CovertSwarm. Not only do we actively share our knowledge and experience, but we network with experts in a range of specialisms, and only…
Critical RCE in DrayTek Routers (CVE-2022-32548)
We would like to bring your attention to the following critical remote code execution vulnerability we have recently become aware of which affects the following DrayTek products: The vulnerability allows remote unauthenticated attackers to execute commands on the affected routers…
Why a cyber value proposition should be part of your business strategy
Whatever your industry, it’s critical to think about your cyber security posture in the right way.
Critical vulnerabilities identified in VMware products (CVE-2022-31656)
We would like to bring your attention to the following critical vulnerabilities we have recently become aware of which affects the following VMware products: VMware is urging all users of the above applications to apply the latest patches in order…
DEF CON 30: what it is and where to find us
When it comes to your cyber security, you have to keep ahead of the curve.
Exploiting Microsoft Windows 11 via Process No-Hollowing
An adapted technique to bypass Managed Detection and Response (MDR) and Endpoint Detection and Response (EDR) solutions.
Working at CovertSwarm: One Hive Member’s Experience
Jack Smith is a Cyber Security Consultant and Red Team Hive Member and one of our newest additions to the Swarm. Over the past 8 months Jack has proved invaluable, with his cyber security skills matched only by his passion for the industry.
Constant offensive security – How does it all work?
Luke Potter, CovertSwarm’s COO, explains everything you need to know about our continuous approach to offensive security. Contact us to learn more about how we support organizations around the world to increase their security posture and outpace cyber threats.