

The one where we signed up to the admin pool.
One cloud misconfiguration hid among 2,500 triggered rules. An identity pool that let anyone register an account ultimately reached 34,000 production records.
One cloud misconfiguration hid among 2,500 triggered rules. An identity pool that let anyone register an account ultimately reached 34,000 production records.
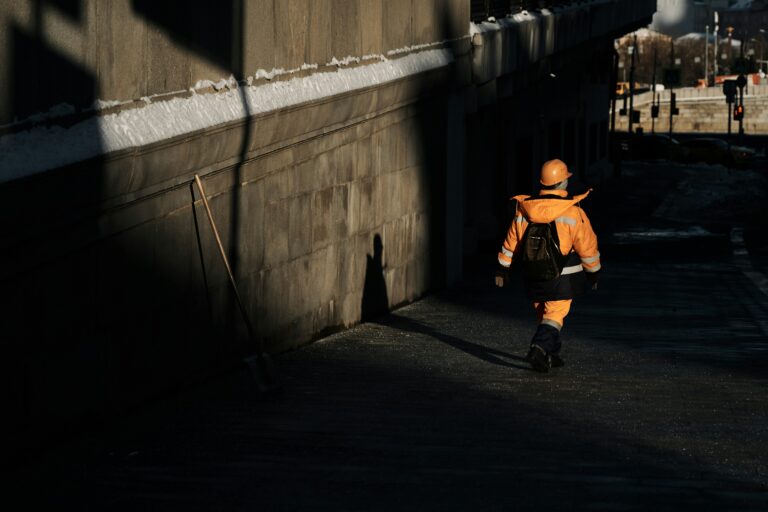
Hi-vis jackets, a clipboard, and a story about counting sockets. That's all it took for a tailgating attack to bypass reception, reach the C-suite, and walk out with a corporate laptop, completely unchallenged.
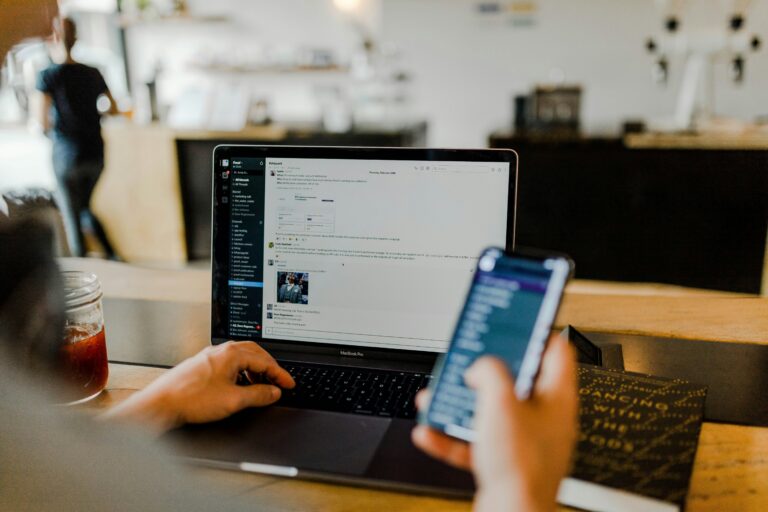
A GitHub token, posted in Slack and left unrotated for over a year, gave us complete control over the organization's software supply chain, from proprietary code to every downstream build.
A year-long business email compromise campaign built entirely on AI social engineering: lookalike domains, a fabricated authority figure, and patient trust-building. No malware, no exploits, just an inbox and the words "this is approved."
Two VMs, one rule: don't get caught. We tunneled in through an overlooked port, found cleartext credentials, and used pass-the-hash to compromise nearly every device in the subnet, undetected.
We plugged a device into their network with nothing. No credentials, no map, no inside knowledge. Five days later, we had domain admin, and no alert had ever fired.
During an OSINT engagement, we found a forgotten login page still pulling a JavaScript file. Inside: admin credentials in plain text, and full production database access.
A routine assumed compromise scenario at a fintech uncovered a predictable onboarding password pattern. It led to password cracking across more than 90% of employee accounts, including the CEO's, proving a single overlooked process can undo an otherwise strong security program.