
Blog
Stay ahead with news, opinion and research from the Swarm.

Academy Launches Second Intake
CovertSwarm's Academy is opening the 2024 intake. Apply and start your cybersecurity journey as an ethical hacker.
Combining regulation with real-world security assurance: DORA and NIS2
Whether you’re a local financial startup or a multinational food distributor, understanding how DORA and NIS2 may affect your organization is vital. Both regulations are now in force.
CovertSwarm named by Clutch among Top 100 Fastest-Growing Companies
Clutch has recognized us for achieving one of the highest revenue growth rates from 2022 to 2023.
The Sunday Times – Best Places to Work
We have been included in The Sunday Times Best Places to Work 2024 list.
Ellie Lancaster joins as Head of People and Culture
Ellie joins to continue developing the industry-leading culture CovertSwarm is being recognized for.
K8s – Pod to Node Escape Techniques
In this article we are exploring the breakout of a pod, to gain access to a node. This is performed by attackers to elevate their privileges in a Kubernetes environment.
Rishikesh Bhide joins CovertSwarm as Head of Engineering
Rishikesh joins CovertSwarm to accelerate the organization’s engineering capabilities and product strategy as part of its rapid growth trajectory.

Louis Blackburn joins as Operations Director
Louis joins CovertSwarm from Lloyds Banking Group with an extensive background in red teaming, becoming the latest senior hire as part of the organization’s rapid expansion and growth strategy
CovertBrew February Edition
Our first ever CovertBrew networking event.
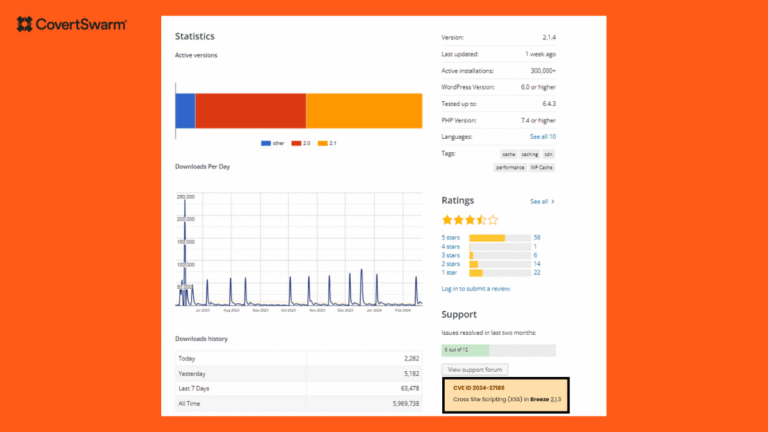
Discovering WordPress Vulnerabilities to Make it Safer
Breeze - WordPress Cache Plugin
Exploiting CVE-2023-5043 and CVE-2023-5044 to overtake a Kubernetes Cluster
In this blog we are exploring two new CVE's that exploit an issue in the NGINX controller when NGINX is used for ingress control.
Uncloaking Radio Frequency Identification (RFID)
Demystify RFID with insights on components, tag types, modulation, and use cases. A concise guide to the intricate world of RFID.
A journey into Badge Life
Explore CovertSwarm's Badge Life journey from Defcon 30 chaos to Defcon 31 triumphs. Join the hardware hacking adventure in this article!
Gaining Initial Access in a Kubernetes Environment (part 2)
Explore initial access in Kubernetes: Uncover application vulnerabilities, compromised images, and cloud credential misuse in Kubernetes environments.
Exploring the Kubernetes Architecture from an Offensive Viewpoint (part 1)
Explore the essentials of Kubernetes: From its Google origins to a key tool in modern cloud-native development, learn about its architecture, API server, nodes, and security aspects.
Persistence Attack in Active Directory: The Golden Ticket Attack
Delve into the Golden Ticket Attack in Active Directory: a key APT method. Discover its workings, countermeasures, and detection to protect your network.
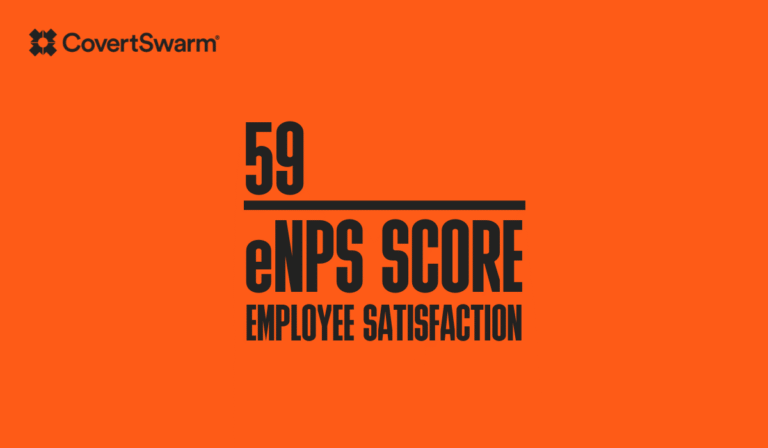
Our first Employee Net Promoter Score in review
CovertSwarm ranked as one of the leading industry employers after recording our first ‘excellent’ score
CovertSwarm named on the Startups 100 Index
Startup.co.uk has recognized us as one of the UK’s leading start-ups and part of the next generation of game changers.

CovertSwarm strengthens leadership team with three key senior appointments
We're preparing for another year of growth in 2024
What is Breach and Attack Simulation (BAS)?
Read our guide to find out what Breach and Attack Simulation (BAS) is, how it works, why and how it’s important, and some best practices.
What is vulnerability scanning and why is it important?
Read our comprehensive guide on vulnerability scanning, including what it is, why it’s important, how it works & best practices for organizations.
We’ve been named a CISO Choice Awards finalist
The program recognized CovertSwarm as one of the world’s leading cybersecurity solutions
Web application vulnerability scanning, in the palm of your hands
At CovertSwarm we pride ourselves on being able to provide the Portal as a centralized platform for managing and identifying risk to your organization. Following on from our recent blog post on why web application security and why it is…
What is web application security, and why is it important?
Read our guide on web application security, which includes what it is, why it’s important, how it works & best practices & useful strategies.