




You deserve
to be hacked.
Successful companies like yours are constant targets for attackers. Those who take security seriously don’t just test their defences once a year.
They subscribe to CovertSwarm.
Can your security programme survive an attack?
You bought the tests, the tools and the scanners. You tell them where to look, and they’ll tell you what they found. None of them can tell you what will break your business.
Threat actors target your whole organisation. Your people, systems
and suppliers. You don’t need more findings. You need proof of where you really stand. For your board. For your regulator. For yourself.
How confident are you?
The only way to be confident is to face a real attacker.
CovertSwarm is the APT built to target you. Our offensive security subscription gives you a Swarm of ethical hackers that thinks, acts and strikes like a real attacker.
Your Swarm attacks your whole organisation across physical, social, and digital environments within safe guardrails, proving how far a real attacker could go and showing you how to fix the weaknesses.
You get direct team access and board-ready evidence of where you stand. Over 100 security leaders subscribe to CovertSwarm.
Are you ready? Let’s find out.
It takes a Swarm to outpace threats.
While you plan your next test, attackers are probing everything: your systems, your people, and your suppliers. They don’t care about scopes or findings. They’re focused on objectives.
And they won’t send a nice PDF when they’re done.
Relentless adversarial pressure.
Forget rigid scopes and waiting weeks for a report. We give you a relentless adversary, attacking, probing, and exposing weaknesses before real attackers do. And if we can’t break in, you’ll know your security investments are working.
The closest thing to the threats you face every day.
Persistent by design.
A test ends with a report. Your Swarm doesn’t stop there. Within your agreed guardrails, they’ll continue to attack until they reach their objectives.
Your own APT, built to target you, that changes and adapts with you.
One subscription is all you need.
Digital. Social. Physical. Compliance. Regulatory testing. Get it all in one simple subscription for less than the cost of a single security hire.
Simpler billing and less procurement so you can keep moving faster.
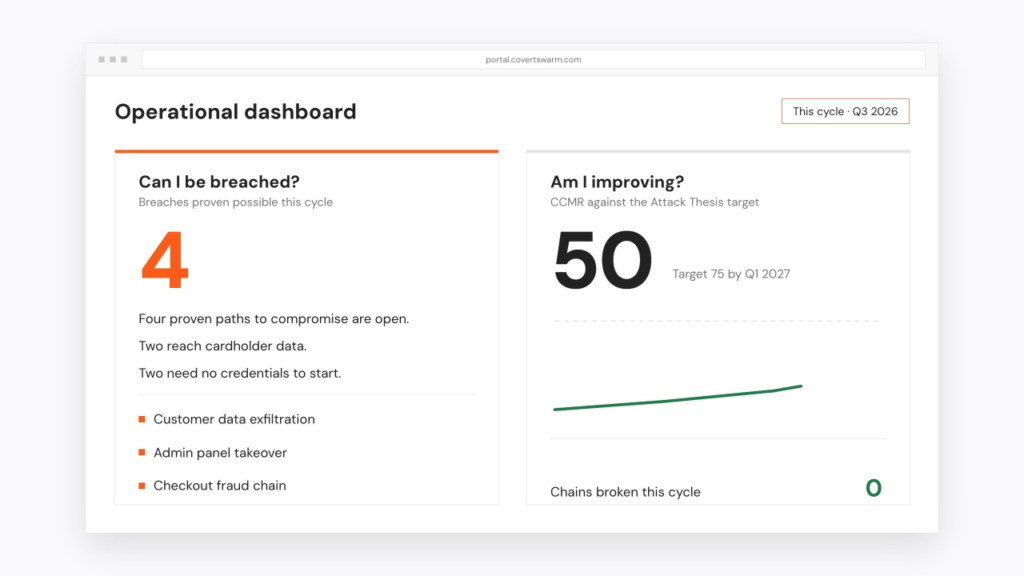
Your direct line to the Swarm.
See what your Swarm is targeting, what they have proven and what needs fixing. One shared view of the attacks and your response, all in the CovertSwarm portal.
Stories from the Swarm
These stories are real, but the names are redacted. We’ll tell you how we uncovered the threats no one else could see, and why constant cyber attack is the best way to outpace cyber threats.
Use Cases
Your biggest security problems each have an attacker behind them. Constant Cyber Attack™ becomes that attacker, so you can see what holds and what to fix.
-
Regulatory and compliance readiness
Compliance is mandatory. Attackers are relentless. Get threat-led, regulator-aligned testing while strengthening real-world resilience.
-
Prove the effectiveness of your security investments
You’ve invested in security. Now demand proof it works. CovertSwarm attacks your technology, people and processes to reveal what stops an adversary, what fails and where to focus next.
-
Secure your AI and agentic systems
CovertSwarm attacks your agents and AI apps to show how attackers could breach them, and what they could reach.
-
Improve resilience against AI-enabled attacks
CovertSwarm prepares you to meet the pace and intensity of AI-enabled attackers.
-
Unknown risk discovery
CovertSwarm strengthens your security posture by continuously attacking, exposing, and mapping currently unknown risks.
Latest posts
php2shell: moving beyond a lab proof of concept to code execution with ASLR enabled
The Swarm developed a working exploit for php2shell (CVE-2026-109618 and CVE-2026-109619). It achieved unauthenticated remote code execution with address space layout randomisation (ASLR) enabled and PHP error display disabled, in our tested AArch64 PHP 8.5.11 environment running Apache with mod_php.
Release: local checker for PHP2Shell (CVE-2026-109618 and CVE-2026-109619)
An Open Source host-local vulnerability checker for CVE-2026-109618 and CVE-2026-109619 (PHP2Shell).
Stop testing.
Start knowing.
You’ll know exactly where you stand, and you’ll be able to prove it. To your board, your regulator, and yourself.
Transform to a proactive, continuous offensive security programme
Your budget is aimed at the risk that matters, not the one you were handed
You show the board what security prevented, not a request for more
Security clears the way for the business to move faster
You enter the boardroom in command
It starts with a 30-minute Attack Discovery call.
No access to your systems required.